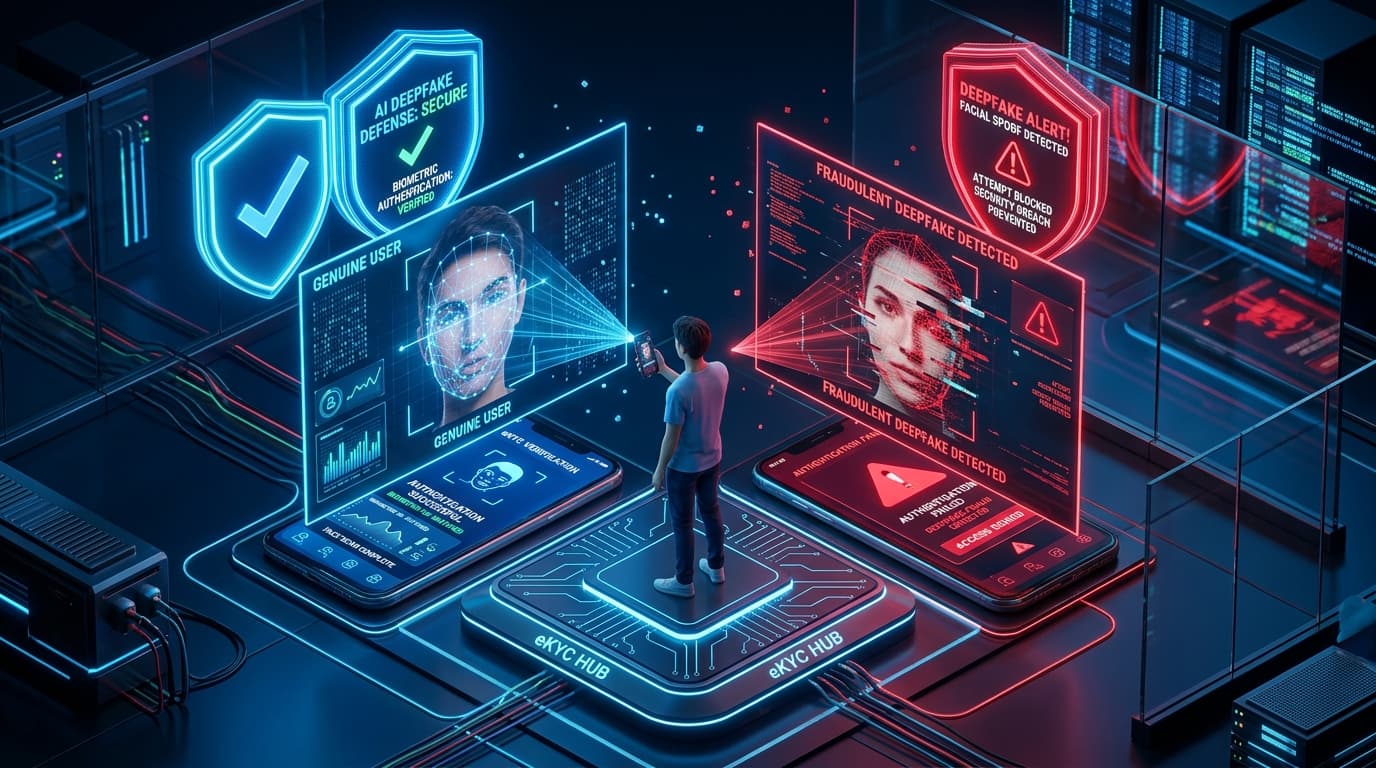
Traditional eKYC relies on a linear sequence: "ID OCR → Selfie Capture → Liveness Detection → Face Matching → Approval". However, if the captured selfie is an AI-generated video or injected via virtual camera tools, conventional facial matching completely collapses. Next-gen eKYC must verify not just facial similarity, but physical human presence, sensor authenticity, media manipulation artifacts, and data transmission integrity.
The Fundamental Flaw in Legacy eKYC
For financial institutions, licensed money lenders, virtual banks, and FinTech platforms, standard eKYC typically operates as:
The critical question is: If the received selfie stream is an AI-synthesized deepfake or an injected media file rather than an authentic optical sensor capture, standard 1:1 face matching and basic liveness checks are easily bypassed.
1. How Deepfakes Attack eKYC: Four Primary Vectors
Modern fraud syndicates employ structured and sophisticated AI methodologies to deceive eKYC systems:
AI Face Swap
Attackers swap their own live facial features with the target victim's face in real-time or offline:
If the system only computes 1:1 facial biometric distance, the AI-rendered face will match the victim's ID card with high confidence.
AI-Generated Faces
Using GANs or Diffusion models, AI can fabricate entirely non-existent persons or synthesize dynamic video feeds from a single static photo. Looking realistic does not mean the person is physically standing in front of the lens.
Dynamic Deepfake Video
Attackers animate avatars to accurately mimic interactive prompts:
This severely impairs simple, predictable "please blink" or "please turn left" challenge-response mechanisms.
Digital Injection Attack
Highest RiskThis is the most clandestine vector. Fraudsters do not need to hold a screen in front of a smartphone camera (Presentation Attack). Instead, they inject synthesized media directly into the OS driver or network layer:
The eKYC system believes it is receiving a raw camera feed, but is actually processing a pristine, pre-rendered deepfake video stream.
2. Why Traditional eKYC is Insufficient: Comparing Module Limitations
Each standalone module in an eKYC pipeline was designed for a distinct purpose and cannot solve broader systemic attacks alone:
| Technology | Primary Verification Goal | Cannot Solve Alone |
|---|---|---|
| OCR / ID Verification | Document data & format validity | Physical human presence |
| Face Matching | Facial feature similarity (1:1) | AI Deepfake synthesis detection |
| Legacy Liveness | Visual liveness motion | Digital Injection & Virtual Cameras |
| Deepfake Detection | Media manipulation artifacts | Real-world identity legitimacy |
| Device Attestation | App runtime on untampered hardware | Whether the user is the true owner |
| Risk Engine | Multi-dimensional risk scoring | Relies entirely on upstream signals |
The conclusion is straightforward: Deepfake defense cannot rely on a single technology; it requires Defense-in-Depth (Multi-Layer Security).
3. Methods to Block Deepfakes: Passive Liveness Detection
Passive Liveness Detection
Passive Liveness requires no user cooperation. In a split second as the user looks at the camera, deep neural networks analyze intricate physical optical cues:
This mitigates attacks from printed photos, screen replays, 3D silicone masks, and unrendered fake videos.
4. Active Liveness / Challenge-Response: Value and Limitations
Active liveness issues randomized dynamic prompts requiring real-time user interaction:
Implementing unpredictable multi-step challenges (e.g., "Turn left 30 degrees, then blink twice") significantly raises the bar against pre-recorded replay attacks.
Critical Awareness: Active Liveness ≠ Complete Deepfake Protection
With real-time deepfake rendering engines, AI can dynamically drive facial meshes to follow screen prompts. Active Liveness must not be relied upon as a sole defense.
5. Deepfake Detection: Spatial & Temporal Forensic Analysis
Modern systems deploy dedicated neural networks to detect micro-artifacts across spatial and temporal dimensions:
Face-Level Forensics
- •Boundary Blending Artifacts: Feathering, blur, or warping along jawlines and hairlines.
- •Feature Deformations: Unnatural pupil geometry, tooth texture blending, and sclera color shifts.
- •Micro-Expression Discordance: Anatomical inconsistencies across facial muscle groups.
Video-Level Forensics
- •Temporal Coherence: Frame-to-frame lighting flicker, jitter, and ghosting.
- •Lip-Sync Phasing: Phase discrepancies between phonetic acoustics and lip motion.
- •GAN / Diffusion Fingerprints: Characteristic frequency domain energy peaks and reconstruction noise.
6. The Crucial Battleground: Defending Against Digital Injection
In modern eKYC, the question is not merely "Is this face a deepfake?", but fundamentally:
"Was this video captured live by an authentic, physical camera sensor?"
Device Attestation & Environment Integrity
Runtime Environment Auditing
Detect virtual cameras, OS emulators, jailbroken/rooted devices, screen capture tools, and runtime memory hooking (e.g., Frida, Xposed).
Hardware-Backed Attestation
Leverage Apple App Attest and Google Play Integrity to guarantee genuine device origin:App → Genuine Device → Genuine Camera → eKYC Server
📌 FIDO Alliance Requirements: In FIDO Face Verification benchmarks, Injection Attacks are evaluated independently from Presentation Attacks and Biometric Matching.
7. Secure Capture: Building an End-to-End Trusted Pipeline
To prevent media hijacking across the capture chain, high-security systems establish trusted cryptographic capture:
Adhering to NIST Authenticated Protected Channels, each video frame is signed with hardware asymmetric keys and timestamps before transmission, eliminating Man-in-the-Middle (MITM) tampering.
8. Comprehensive eKYC: The 8-Step End-to-End Defense Architecture
Modern financial-grade eKYC is an orchestrated 8-step holistic process:
Step 1 — Document Verification
Optical OCR, Real-Doc dynamic hologram inspection, MRZ/NFC chip PKI digital signature verification to authenticate physical documents.
Step 2 — Trusted Face Capture
Launch hardware-secured camera sensors via native SDK and bind hardware sensor metadata.
Step 3 — Liveness / PAD
Execute ISO/IEC 30107-3 compliant passive and active challenge checks to verify living 3D human presence.
Step 4 — Deepfake Detection
Neural network analysis for edge artifacts, temporal jitter, GAN/Diffusion fingerprints, and synthetic manipulations.
Step 5 — Digital Injection Detection
Block virtual cameras, emulator injections, memory hooks, and network stream interception.
Step 6 — Face Matching
Compute high-precision 1:1 facial biometric vectors comparing live face with authenticated ID photo/chip image.
Step 7 — Comprehensive Risk Engine
Aggregate identity risk, device score, liveness confidence, deepfake rating, credit fraud telemetry (MCRA), and behavioral patterns.
Step 8 — Intelligent Decisioning
Automated routing: Low-risk 'Instant Approval', borderline 'Human Review', and high-risk 'Immediate Rejection'.
9. Emerging Threat: Face Morphing Attacks
Beyond real-time Deepfakes, eKYC must guard against Face Morphing, where facial images of two different individuals are algorithmically blended:
If placed on an official ID card, both individuals A and B might match and pass automated facial recognition systems.
NIST has published specialized Morph Detection guidelines. Enterprise eKYC must integrate Morph Attack Detection (MAD) algorithms to detect landmark blending and photometric distortions.
10. The Human-in-the-Loop Baseline
No AI algorithm achieves 100% accuracy. When facing ambiguous signals, the system should escalate cases for human verification:
Escalating borderline cases to Tier-2 Human Review balances rigorous fraud prevention with minimal False Rejection Rates (FRR) for legitimate users.
Enterprise Anti-Deepfake Implementation Guide: The 4-Tier Defense Matrix
To assist financial institutions, licensed money lenders, and FinTech teams with structured technical upgrades, we deconstruct anti-deepfake capabilities into a 4-Tier Defense Stack. Organizations can deploy modules based on their specific risk appetite:
Endpoint Security & Anti-Injection Layer
🛠️ Core Defenses:Direct camera driver binding, real-time virtual camera interception, emulator/jailbreak detection, runtime memory hooking (Frida) defenses, and Apple App Attest / Play Integrity cryptographic tokens.
🎯 Attack Neutralization:Completely cuts off pre-recorded video injection and synthetic stream tampering via low-level OS pipes (Digital Injection).
Biometric & Multi-Spectral PAD Layer
🛠️ Core Defenses:3D spatial geometry passive liveness, corneal specular reflection consistency, microvascular blood flow analysis, temporal jitter verification, and GAN/Diffusion spectral anomaly recognition.
🎯 Attack Neutralization:Real-time face swaps, ultra-high-definition screen replays, and 3D silicone biometric masks.
Hardware PKI & Optical Forensics Layer
🛠️ Core Defenses:Smartphone NFC direct reading of HKID smart card chips (ICAO 9303 PKI digital signature verification & high-res facial extraction), alongside Real-Doc dynamic hologram angular refraction audits.
🎯 Attack Neutralization:Physical high-replica counterfeit ID cards, headshot alteration attacks (e.g., eMPF case vector), and surface optical tampering.
Authoritative Ecosystem & Risk Engine Layer
🛠️ Core Defenses:HKSAR "iAM Smart+" official digital identity authentication, Credit Data Smart (MCRA / CDS) credit history cross-referencing, telecom real-name matching, and same-name bank mandate (eDDA).
🎯 Attack Neutralization:Synthetic identity theft, money laundering mule accounts, and cross-lender fraud.
Phased Implementation Roadmap for Financial Institutions
11. Conclusion: Rebuilding Digital Trust in the Age of Generative AI
When seeing is no longer believing, financial institutions relying on legacy 2D photo matching face existential fraud and compliance risks.
Upgrading to a multi-layered architecture—combining trusted capture, chip-level PKI verification, deep forensic AI, and authoritative data cross-referencing—is the only viable path forward.
Recommended Solutions & API Gateways
eKYC Digital Identity Verification
Omnichannel eKYC covering WhatsApp, Web, and Native Apps with 3D Liveness and smart HKID verification.
Real-Doc Anti-Fraud & 3D Liveness
AI-driven forensic analysis of hologram reflection, edge tampering, and micro-typography to block Deepfakes.
NFC Smart HKID Reader
Hardware-grade PKI verification reading ICAO digital signatures directly from smart card chips.
iAM Smart Integration Solution
Connect to HKSAR 'iAM Smart+' official digital identity authentication and compliant digital signing APIs.
Related Articles & Technical Insights
Curated fintech, regulatory guides, and industry insights
Claude Introduces eKYC: Use Cases and Future Trends in AI Identity Verification
In-depth analysis of Anthropic's Claude introducing eKYC identity verification. Explore architectural design, 4 core use cases, and 6 future industry predictions.
The Relationship Between eKYC and Passkey: Who You Are vs. Are You Really You
In-depth analysis of the relationship between eKYC and Passkey. Understand how identity verification and passwordless authentication collaborate to build end-to-end digital identity security.
The Cornerstone of Future Finance: Development and Application of eKYC
Explore the evolution, technical framework, and regulatory standards of eKYC in modern financial services.